Bug #11770
openCorrect User Attribution & Null-Safety in Product Quote Admin Approval
100%
Description
In the
acceptQuoteViaAdmin product quote controller.js file
endpoint:
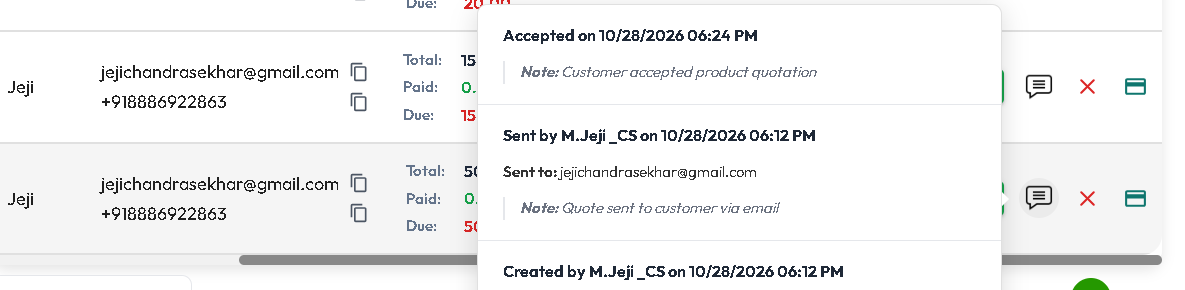
When an administrator manually approves a product quotation, the audit trail records:
performedBy: quote.customer._id,
note: "Customer accepted product quotation"
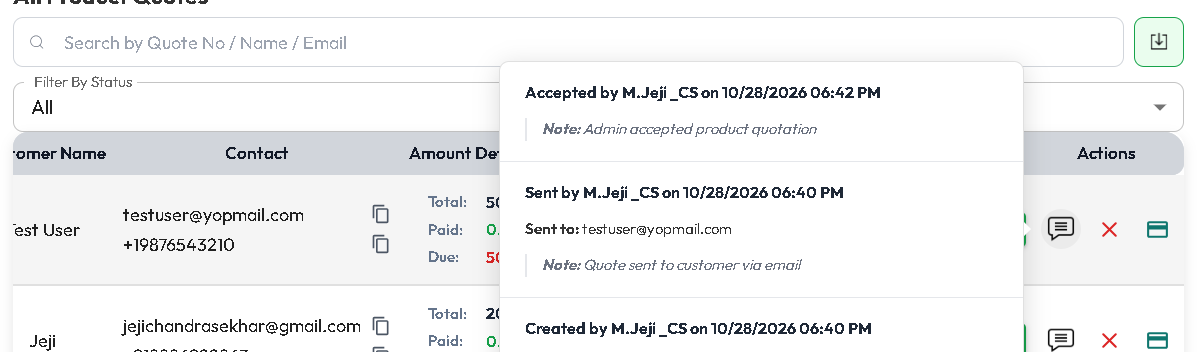
This creates a false audit log claiming the customer accepted it directly, masking the admin's action (req.user.id).
If quote.customer is null or undefined (e.g., if the client profile was deleted or detached), dereferencing quote.customer._id throws an unhandled runtime error (TypeError: Cannot read property '_id' of null), crashing the request with a 500 error.
Acceptance Criteria
AC 1.1 (Accurate Attribution): Given an authenticated admin approves a product quotation via acceptQuoteViaAdmin, When the quote status updates to "approved", Then the actionHistory record MUST set performedBy to req.user.id (or userId) and the note MUST clearly state "Admin approved product quotation on behalf of customer".
AC 1.2 (Null-Safety): Given a product quotation whose customer reference is null or unpopulated, When an admin approves it, Then the operation MUST proceed without throwing a TypeError, falling back gracefully to null or a placeholder client reference.
AC 1.3 (Audit Log Inspection): When fetching action history via getActionHistory, the approval entry must render the admin's name/ID rather than the customer's.
3. Recommended Implementation Note
javascript
// Replace lines 2271-2281 with:
quote.actionHistory.push({
action: status === "approved" ? "admin_approved" : "draft",
performedBy: userId, // from req.user.id
note: status === "approved"
? `Admin approved product quotation on behalf of customer (${quote.customer?.firstName || "N/A"} ${quote.customer?.lastName || ""})`.trim()
: "Admin marked product quotation as draft",
timestamp: new Date(),
changes,
});
Files
Subtasks
Related issues